Another CASL fine

The Canadian Radio-television and Telecommunications Commission (CRTC) announced today that Porter Airlines had agreed to pay a fine of $150,000 for violations of the Canadian Anti-Spam Law (CASL).
After investigating the airline, CRTC found multiple violations of the statute. These violations include no unsubscribe link or the unsubscribe link was not prominent enough.
Some of the messages at issue failed to have proper identification. Finally, Porter Airlines couldn’t prove consent for at least some subset of the subscribers.
This is another in a series of enforcement actions where CRTC fined companies for violations of CASL. But none of those enforcement actions really seem overly punitive. There were multiple people publicly concerned about CRTC aggressively fining companies and even driving them out of business. These concerns now appear to be unfounded. Certainly, CRTC is enforcing the law but in a way to help companies come into compliance with it.
Another major concern some individuals had was the private right of action under CASL. I recently attended a conference where one of the talks was related to CASL and enforcement. What was said there is that there are some constraints on bringing a case. For instance cases can’t be brought in lower courts, they have to be brought in the provincial (I think) courts. This puts an additional burden on plaintiffs. Reading between the lines, my impression was this was intended by the regulatory agency and lawmakers to stop nuisance type suits, but allow for real action when needed.
Finally, I have yet to hear about any enforcement action that resulted in fines for corporate officers rather than the corporation as an entity.
All in all, the chicken littles claiming that this law was going to drive email marketers out of business seem to have been wrong. In fact, when I asked a question during the session “have you heard of any companies stopping marketing in Canada due to CASL” the first response was a scoff. This was not the purpose or intent of the law, and it doesn’t appear to be enforced that way.
Related Posts

CASL is more privacy law than anti-spam law

Michael Geist, a law professor in Canada, writes about the new CASL law, why it’s necessary and why it’s more about privacy and consumer protection than just about spam.

Read More

Have fun storming the CASL!

I’ve given Humble Bundle my (tagged) email address a bunch of times – as part of purchases, as my username on their website, to download games and books I’ve bought.
And, naturally, they’ve sent me newsletters announcing when they have new sales. Did I check a checkbox or uncheck a checkbox? I don’t remember, and don’t really care. It’s a company I have a real relationship with and have purchased from, they’re sending content I want to see, and I trust them not to misuse my address and to honour an unsubscription request.
So … probably opt-in, and I’m fairly sure they’ve confirmed that it’s my email address. But did they explicitly tell me they’d use my email address for a newsletter? I and my email archive don’t remember that far back, and it’s quite possible that Humble Bundle’s current staff and records don’t either.
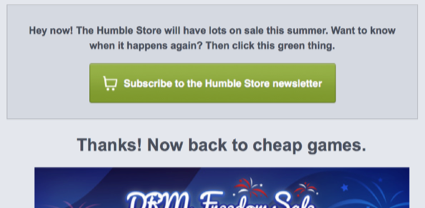
In todays newsletter, right above their talking about their summer sales, they had this:
 
All_Mailboxes__Found_118_matches_for_search_
 
They’re confirming that I want to keep getting newsletters, and stressing why I want to keep getting them. Their database probably dates back to the iron age, or at least 2010, and my clicking on the big, friendly green button both lets them know that I’m an engaged subscriber and lets them record in their database that “Yes! This subscriber has explicitly said they want our newsletters!”.
Gradually adding that information to their subscriber database will let them better make decisions in the future about what content to send, how often, whether to try and reengage with a subset of their subscribers.
Oh, and there’s CASL, of course.
If you or your recipients have a Canadian presence you have a little less than eighteen months to make sure you have documented, explicit consent from any recipients for whom you only have implicit (e.g. business relationship) consent or for whom you’ve lost the original records.

Read More

The DMA: Email marketing or spam?

A few weeks ago, I signed up for a webinar from the DMA. As is my normal process I used a tagged address. I don’t remember any notification that I would be signing up for mail, and I generally do look for those kinds of things. I also know a lot of webinars are used to drive sales processes and I prefer not to waste sales time if I’m not actually looking to purchase.
In recent weeks I have gotten an ongoing stream of marketing messages from the DMA. I’ve tried to opt-out, but the DMA don’t actually want me to opt-out. Each marketing message is a different type of message from a different list. Each list must be opted out of individually.
First it was Conferences, then it was Education, then it was Awards, then Events. I’m trying to figure out what’s next and how many more times the DMA is going to get to spam me before I just turn that address into a spam trap.
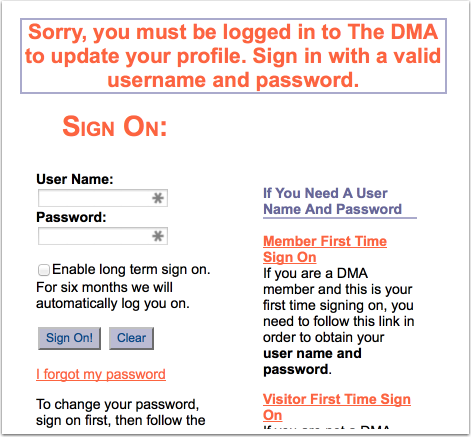
And before you tell me that I can’t make an address a spam trap, think about that a little bit. I never opted this mail in to receive anything but the webinar confirmation. I’ve dutifully opted out each and every time the DMA has mailed me. I’ve even tried to opt-out of all mail. Unfortunately, the DMA has placed the “opt-out of all mail” behind a registration wall, one I cannot get to as I do not have (or want) a DMA account.
DMASignOn
The DMA is sending me mail I did not request and do not want. They have made it impossible for me to determine how much mail I will get. They have made it difficult for me to opt-out of all their mail.
This is an example of bad email marketing. I’m sure that the DMA will tell me this is all permission based email. I disagree. This is an example of the DMA taking permission. This is not an example of a sender asking for permission. I didn’t give permission to be added to all these DMA lists, and I have no way to actually revoke the permission that they took from me.
I signed up for a second webinar with this email address, one related to CASL. The irony is that the DMA’s behavior here is a violation of a number of points of CASL. First, there was no clear opt-in notice on the website. Second, CASL requires parity between opt-in and opt-out. If I opt-in once then I should be able to opt-out once. CASL puts an end to this opt-in once, opt-out dozens of times process.
I wish I could say I was disappointed in the DMA. But I’m barely surprised. Their track record is poor and they have typically fallen on the side of “I have consent until you force me to acknowledge that I don’t.” In this case, the DMA is demonstrating that quite clearly. They will keep spamming and spamming and spamming. I have no doubt were I to actually register an account, they would continue to spam me with “account notifications” that I was unable to opt-out of because they are transactional, membership messages.

Read More