Spamhaus reports Verizon routing hijacked IPs

Late last week Spamhaus published a blog post detailing their investigation into Verizon routing millions of IP addresses hijacked by spammers.
The Spamhaus blog post goes into some detail about what hijacked routing is.

For cybercriminals to make use of their stolen blocks however, a crucial step is to find an Internet Service Provider(ISP) or network with the ability to route these IP addresses to the rest of the Internet by using an autonomous system number(ASN). Also crucial is finding an ISP who won’t look too closely at the highly suspicious routing request. To get the routes to their stolen IP addresses announced, criminals will present forged authorization documents…

Actions like this are why an unknown IP is considered hostile until proven otherwise. I regularly tell clients than 99 times out of 100 when there’s mail from an IP never seen before it’s spam. I’ve often wondered if I’m understating the problem. That is way more than 99 IPs in 100 are sending spam. But I thought that would be an exaggeration and overly aggressive. Seeing the hijacked IPs just being routed through one US provider, though, tells me I am understating the problem.
Nevertheless, this is extremely bad behavior by Verizon and it’s disappointing that they seem unable or unwilling to take action about the spam and abuse coming from their network.
Related Posts

Dealing with blocklists, deliverability and abuse people

There are a lot of things all of us in the deliverability, abuse and blocklist space have heard, over and over and over again. They’re so common they’re running jokes in the industry. These phrases are used by spammers, but a lot of non-spammers seem to use them as well.
The most famous is probably “I’m sure they’ll unblock me if I can just explain my business model.” Trust me, the folks blocking your mail don’t want to hear about your business model. They just want you to stop doing whatever it is you’re doing. In fact, I’m one of the few people in the space who actually wants to hear about your business model – so I can help you reach your goals without doing things that get you blocked.
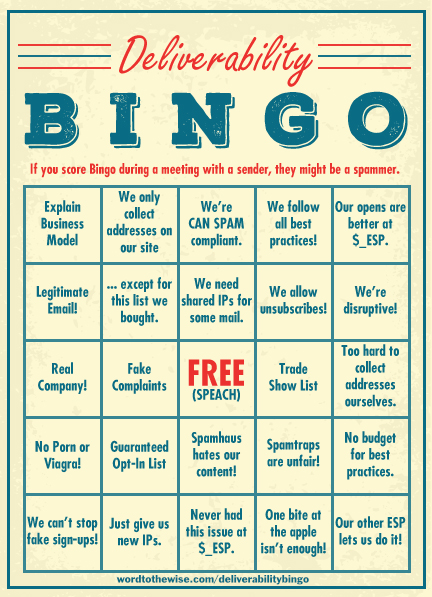
A few months ago, after getting off yet another phone call where I talked clients down from explaining their business model to Spamhaus, I put together list of phrases that senders really shouldn’t use when talking to their ESP, a blocklist provider or an abuse desk. I posted it to a closed list and one of the participants put it together into a bingo card.
bingo__email__save_1
A lot of these statements are valid marketing and business statements. But the folks responsible for blocking mail don’t really care. They just want their users to be happy with the mail they receive.

Read More

August 2015: The month in review

It’s been a busy blogging month and we’ve all written about challenges and best practices. I found myself advocating that any company that does email marketing really must have a well-defined delivery strategy. Email is such vital part of how most companies communicate with customers and potential customers, and the delivery landscape continues to increase in complexity (see my post on pattern matching for a more abstract look at how people tend to think about filters and getting to the inbox). Successful email marketers are proactive about delivery strategy and are able to respond quickly as issues arise. Stay tuned for more from us on this topic.
I also wrote up some deliverability advice for the DNC, which I think is valuable for anyone looking at how to maintain engagement with a list over time.  It’s also worth thinking about in the context of how to re-engage a list that may have been stagnant for a while. A comment on that post inspired a followup discussion about how delivery decisions get made, and whether an individual person in the process could impact something like an election through these delivery decisions. What do you think?
As we frequently point out, “best practices” in delivery evolve over time, and all too often, companies set up mail programs and never go back to check that things continue to run properly. We talked about how to check your tech, as well as what to monitor during and after a send. Josh wrote about utilizing all of your data across multiple mail streams, which is critical for understanding how you’re engaging with your recipients, as well as the importance of continuous testing to see what content and presentation strategies work best for those recipients.
Speaking of recipients, we wrote a bit about online identity and the implications of unverified email addresses in regards to the Ashley Madison hack and cautioned about false data and what might result from the release of that data.
Steve’s in-depth technical series for August was a two-part look at TXT records — what they are and how to use them — and he explains that the ways people use these, properly and improperly, can have a real impact on your sends.
In spam news, the self-proclaimed Spam King Sanford Wallace is still spamming, despite numerous judgments against him and his most recent guilty plea this month. For anyone else still confused about spam, the FTC answered some questions on the topic. It’s a good intro or refresher to share with colleagues. We also wrote about the impact of botnets on the inbox (TL;DR version: not much. The bulk of the problem for end users continues to be people making poor marketing decisions.) In other fraud news, we wrote about a significant spearphishing case and how DMARC may or may not help companies protect themselves.

Read More

Finally! Spam has a purpose

omrayspam_kabekAuthor Julie Czerneda posted about some of her writing techniques on Jim C. Hines’ blog today. Julie is one of my favorite authors. She’s a biologist so her science writing flows well for me. Too many folks try to write biology and get little nitpicky details wrong and it can disrupt the whole book for me. I spend way too much time thinking about the actual biology and lose track of the plot.
One part of her post stood out and made me smile, though.

Read More