Spam, campaign statistics and red flag URLs

It’s not often spammers send me their campaign statistics, but on Tuesday one did.
The spam came “from” news@udemy.com, used udemy.com in the HELO and message-ids and, sure enough, was advertising udemy.com:
 

Received: from udemy.com (unknown [198.20.115.217]) by ...
From: Udemy <news@udemy.com>
Subject: The Photoshop Secret - Master Adobe Photoshop like a Pro!
Message-ID: <20160706031012.1E35F28A6B081174@udemy.com>

 
But the call to action link was a bit.ly URL. Following the clickthroughs, the bit.ly URL redirected to linksynergy.com, which in turn redirected to udemy.com. Nothing too surprising – udemy.com’s users are paying udemy for clicks, which udemy are buying from linksynergy and linksynergy are buying from our spammer. A perfectly normal, spammer-infested affiliate programme.
The spammer might be using bitly to hide the linksynergy URL (linksynergy links on web pages might well be legitimate, but in email they’re a serious red flag and an almost sure sign that the mail is spam), but I think it more likely they’re using it for bitly’s click-through reporting.
One of the nice things about bitly clickthrough reporting is that anyone can see it, just by adding a + sign to the end of it. Our spammer sent https://bitly.com/1JUHIe3, so if we go to https://bitly.com/1JUHIe3+ we can see everything about the clicks on it.
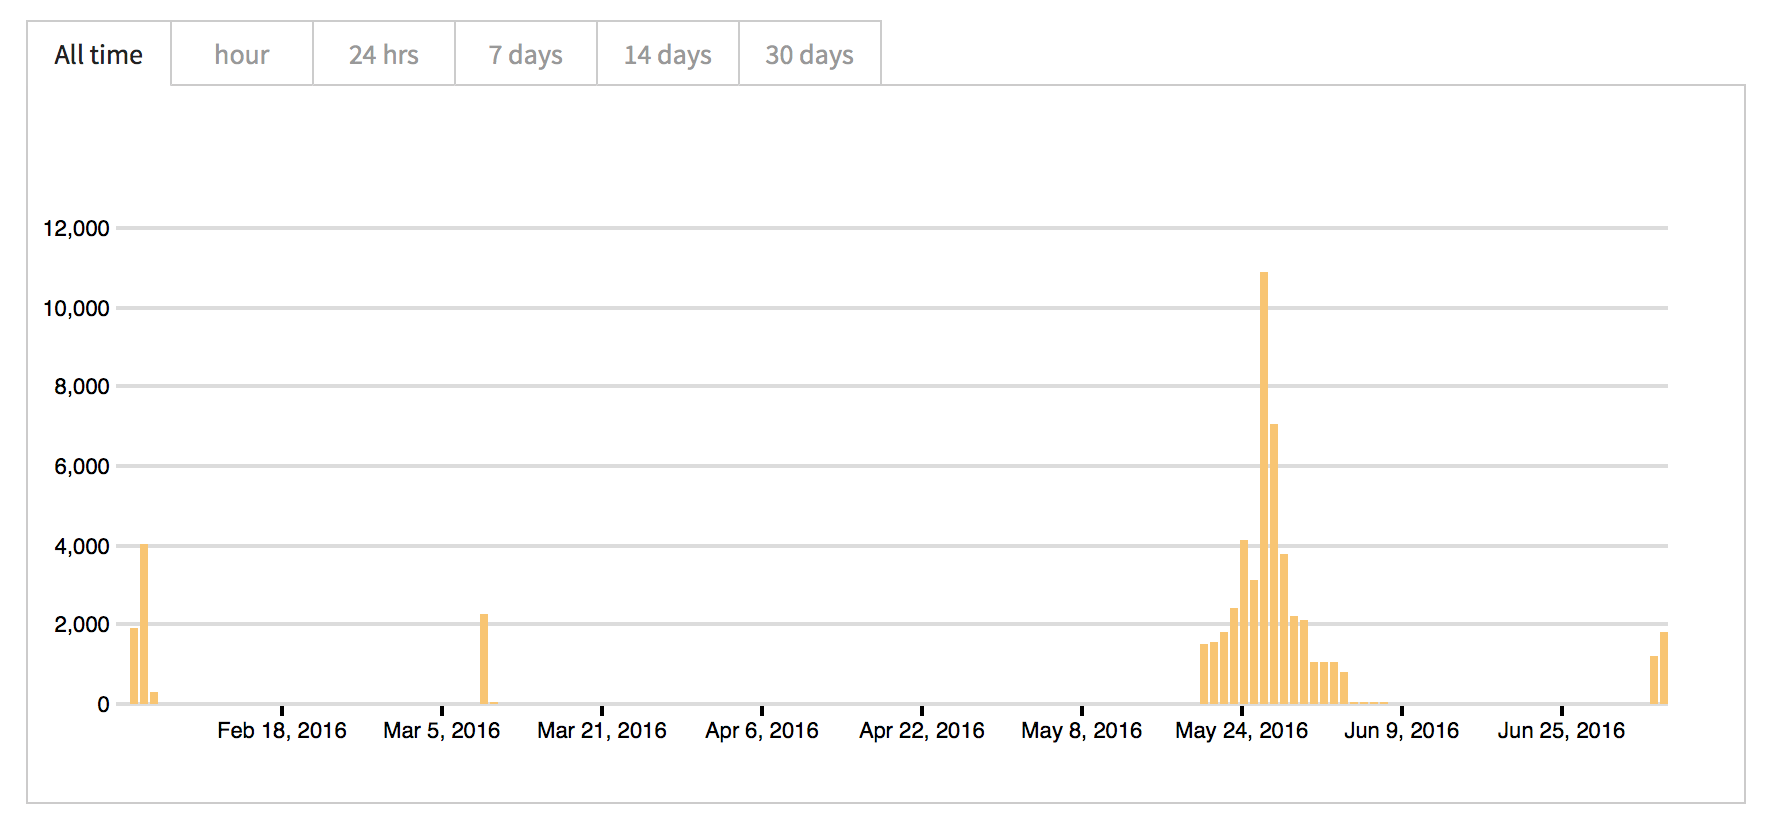
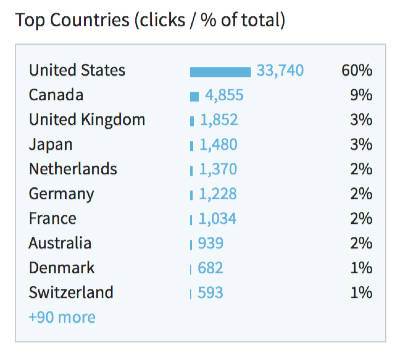
It’s had 56,622 clickthroughs since early February. The vast majority of clicks had no referers, so were likely from email. Of the few hundred that did have referers, they mostly look like webmail. So it’s pretty likely this URL has been used solely for spam.
Bitly__The_power_of_the_link_
 
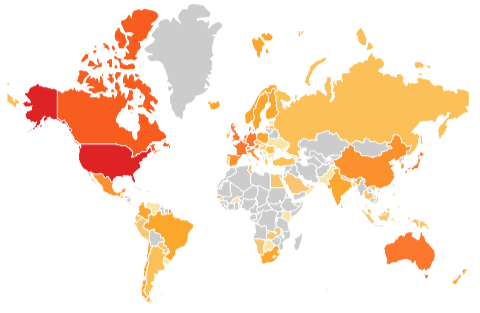
This same URL has been used in four spam campaigns so far, mostly targeted to North America.
Bitly__The_power_of_the_link_
From a spam perspective one of the interesting things is that this URL has been in active use in spam for at least six months, without any of Udemy, LinkSynergy (aka Rakuten) or bit.ly taking any action against it. It’s possible that’s just because none of them knew about it, I guess.
If I’m filtering email this tells me that bitly (or clicksynergy or linkshare) URLs in email are likely to be a problem – and, hence, if I’m sending legitimate email I should avoid using any of that sort of URL in my email. Something we’ve discussed here before.
And if I’m considering running an affiliate programme this is a good example of why I either have to run a very good, well-policed affiliate programme or make a business decision that I’ll make more money from paying spammers to bring in leads than I’ll lose customers due to my poor reputation.
Related Posts

Ugg, a spammer.

I’ve written before about how there is some (I’m sure lovely) woman in the UK who has been connected to my email address. I get a lot of mail for her. Mostly spam. She doesn’t seem to be using the address, but I regularly get mail addressed to MRS. LAURA CORBISHLEY (all caps, always). Typically these messages are advertising various UK stores and products. Sometimes they’re mortgage offers. A few have been sweepstakes only open to UK residents.
ShadyGuyWebsite
I generally forward these spams off to various blocklists with the note it’s my “UK spamtrap” and they take whatever actions seem appropriate to them.
2016-03-21_14-33-39Today, though, I got my first US spam to Mrs. Laura Corbishly. From a Yesmail customer called sanuk.com. I’m getting a website error (they get smacked for spamming already?) but a little research tells me this is shoe company that owns a bunch of brands, including Ugg.
Yes, Ugg a Spammer. They even even have a disclaimer at the bottom of the email telling me they’re a spammer!
2016-03-21_14-35-54
Not so much, no. It appears, though, that the data brokers selling Mrs. Corbishley’s name connected to my email address have figured out that no one ever actually acts on any of their UK offers. So now they’re selling into the US market in hopes that they might entice a purchase?
On a purely nosy level, I’d love to know who was selling the address. First off, I’d love to know where they got this info in the first place. Secondly, what horrible database are they using that keeps name data in all caps? (When I get email to this trap I think they’re shouting at me, as if I’m the one who is wrong about my name. Maybe they think if they yell at me loud enough will I decide I really am the happy wife of Mr. Corbishley of Swindon, UK. )
I do tell clients that it’s useful to remind customers that they signed up for mail, especially if they haven’t mailed for a while. So I know not every email with a “you opted in” reminder is spam, but I only notice those things when I haven’t opted in. It’s something I mostly gloss over if I really did opt-in. I wonder if this is how other folks react to “you opted in” notices, too.
I do recommend the reminder be much more specific than “you opted in at our website.” Give the user a date, a time, something that isn’t just something any company can, and many do, make up.


Read More

Let's talk CAN SPAM

CheckboxEarlier this week I posted about the increased amount of B2B spam I’m receiving. One message is not a huge deal and I just delete and move on. But many folks are using marketing automation to send a series of emails. These emails often violate CAN SPAM in one way or another.
This has been the law for 13 years now, I find it difficult to believe marketers are still unaware of what it says. But, for the sake of argument, let’s talk about CAN SPAM.

Read More

Bad data drives delivery problems

It’s a wild election season here in the US. In the past few presidential elections, email has played a bigger and bigger role in messaging and fundraising. President Obama’s campaign used email effectively, but sent  huge volumes. In fact, the volume was so heavy, it led to a joke on the Daily Show.

Read More