Anatomy of a successful phishing attempt

Earlier this year the Exploratorium was the victim of a phishing attack. They’ve posted an article on what happened and how they discovered and dealt with the issue.
But they didn’t just report on the attack, they dissected it. And, as is appropriate for a organization with a mission of education, they mapped out what they discovered during the investigation.
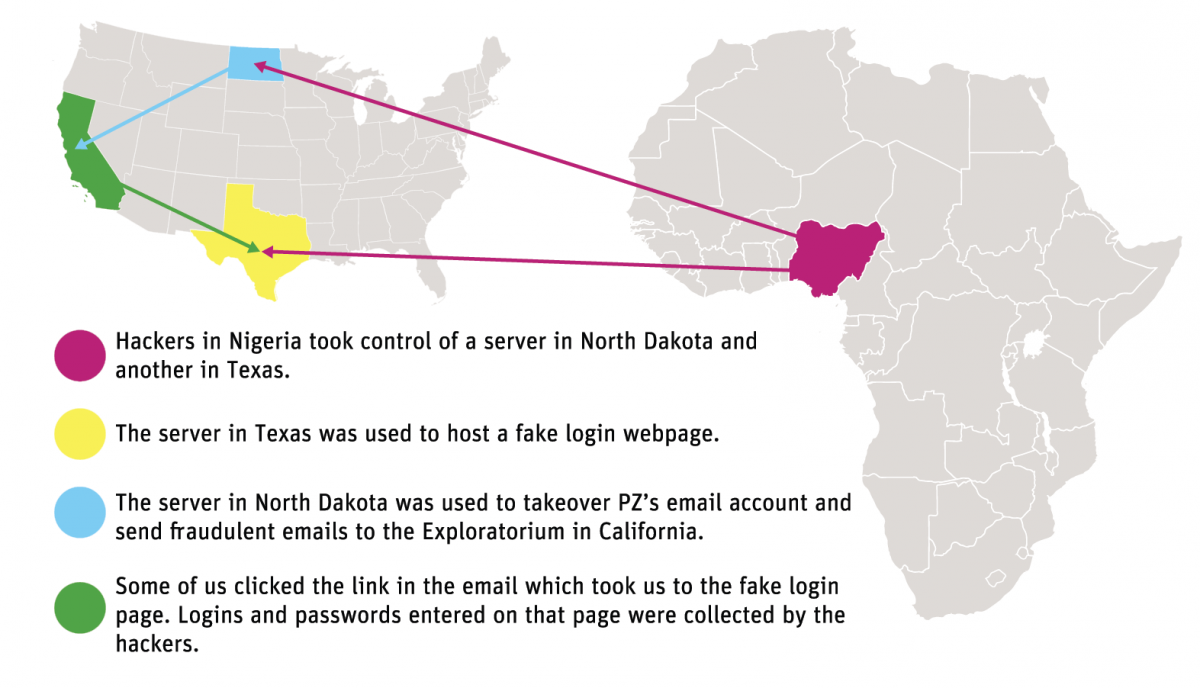
There are a couple of things that stand out to me about this attack. One is that of the more interesting pieces to me is that there was a delay between the compromise and the start of the attack. The Exploratorium calls it “the pivot” and describes it as the hacker deciding what to do next. The second is that the phisher actively interacted with the victim’s account. All new mail was sent to the trash automatically so she wouldn’t see incoming mail. Some mail was actively replied to so more people would click on the message. The phisher took steps to retain access to the account for as long as possible.
One thing that the Exploratorium didn’t see was any actual access to Exploratorium files or information. That may be because the Exploratorium itself wasn’t the target. Once a phisher / hacker has access to the email account, they have access to almost everything in your online life: calendars, bank accounts, credit accounts, the list goes on. Email addresses are our online identity and getting access to the address can open access to so much more.
Quite frankly it can happen to any of us. Earlier this week we received a phishing message that looked very plausible. It came from a law firm, mentioned a subpoena and even had an attachment personalized to our company. The attachment wasn’t opened so we were fine, but I can see how that kind of email might trick someone into getting infected.
We all need to be careful online. Email is a wonderful thing, but it’s insecure. It’s a great way for criminals to get into our space and wreck havoc on our computers and our lives.
 

Related Posts

Are you (accidentally) supporting phishing

One of the themes in some of my recent talks has been how some marketers teach their customers to become victims of phishing. Typically I’m talking about how companies register domains “just for email” and then use those for bulk messages. If customers get used to mail from company.ESP.com and companyemail.com they’re going to believe that company-email.com is also you.
There are other ways to train your customers to be phishing victims, too. Zeltzer security walks us through a couple emails that look so much like phishing that it fooled company representatives. Go take a read, they give a number of examples of both good and bad emails.
biohazardmail
I was a little frustrated that the examples don’t include headers so we could look at the authentication. But the reality is only a teeny, tiny fraction of folks even know how to check headers. They’re not very useful for the average user.
Security is something we should never forget. As more and more online accounts are tied to our email addresses those of us who market to email addresses need to think about what we’re teaching our recipients about our company. DMARC and other authentication technologies can help secure email, but marketers also need to pay attention to how they are communicating with recipients.

Read More

Are you ready for the next attack?

ESPs are under attack and being tested. But I’m not sure much progress in handling and responding to the attacks has been made since the Return Path warning or the Epsilon compromise.
Last week a number of email marketers became aware that attacks against ESPs and senders were ongoing. The shock and surprise many people exhibited prompted my Spear Phishing post on Friday.
The first round of phishing went out on Wednesday, by Friday they were coming from a different ESP. Whether this was a compromised ESP customer or employee it doesn’t matter. ESPs should have reaction plans in place to deal with these threats.
It’s been months since the first attacks. This is more than enough time to have implemented some response to reports of attacks. Yet, many people I talked to last week had no idea what they should or could be doing to protect themselves and their customers.
Last time the attacks were publicly discussed I was frustrated with many of the “how to respond” posts because few of them seemed to address the real issue. People seemed to be pushing agendas that had nothing to do with actually fixing the security holes. There were lots of recommendations to sign all mail with DKIM, implement 2 factor authentication, deploy validation certificates on web properties, or adhere to sender’s best practices.
None of those recommendations actually addressed the gaping security hole: Humans.

Read More

Abuse, triage and data sharing

The recent subscription bombs have started me thinking about how online organizations handle abuse, or don’t as the case may be. Deciding what to address is all about severity. More severe incidents are handled first. Triage is critical, there’s never really enough time or resources to investigate abuse.
biohazardmail
What makes an event severe? The answer is more complicated that one might think. Some of the things that ISP folks look at while triaging incoming complaints include:

Read More