September 2016: The month in email

Happy October, everyone. As we prepare to head to London for the Email Innovations Summit, we’re taking a look back at our busy September. As always, we welcome your feedback, questions, and amusing anecdotes. Seriously, we could use some amusing anecdotes. Or cat pictures.
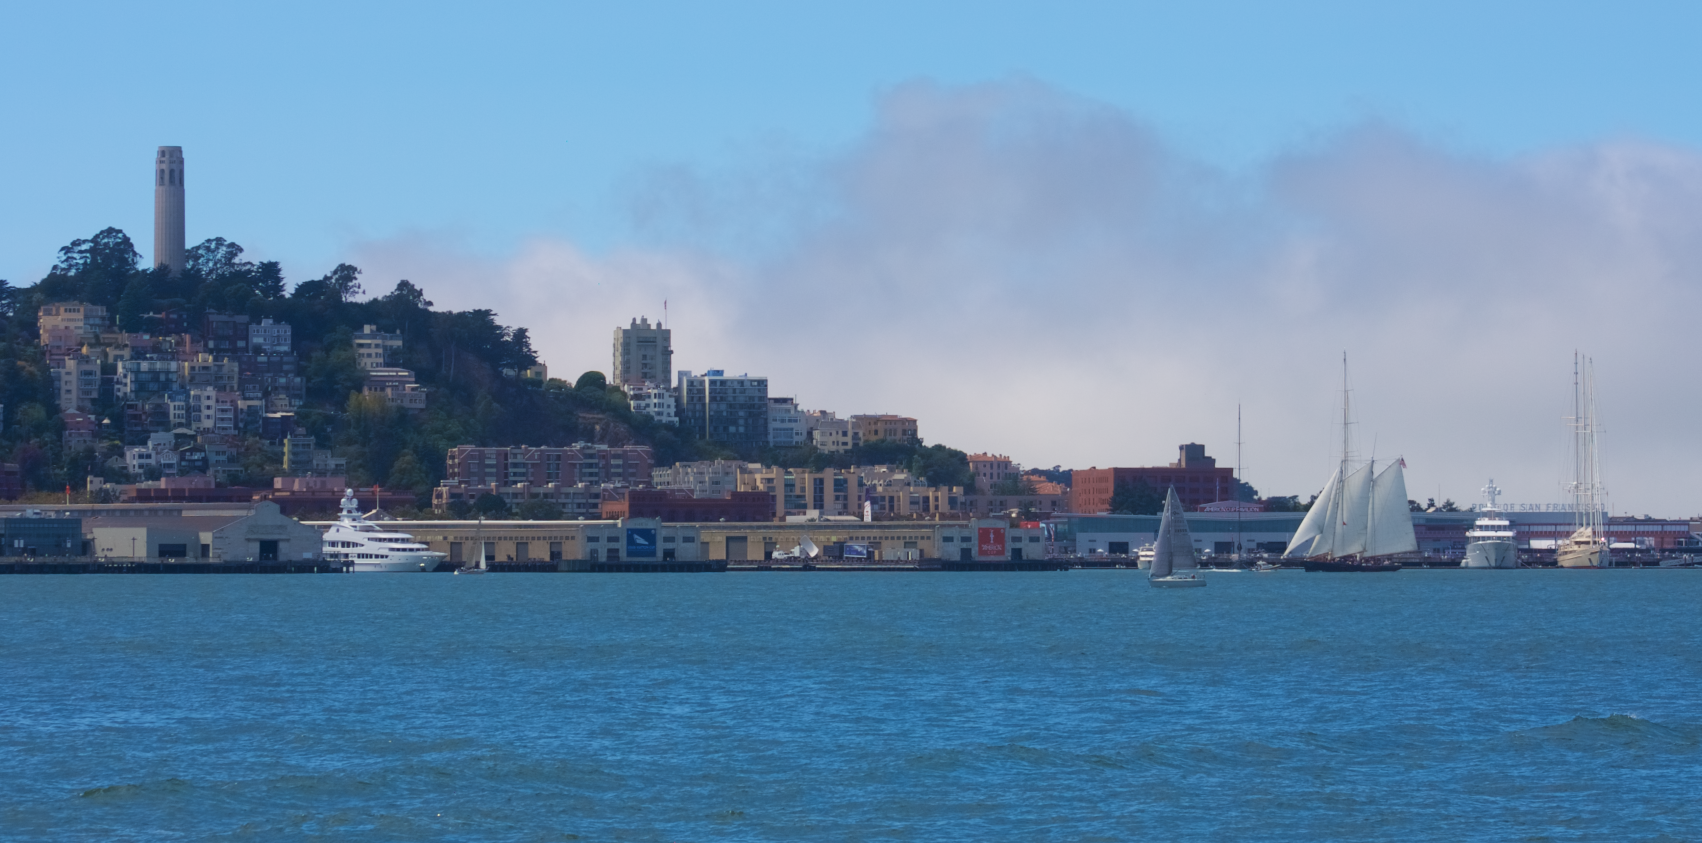
 
San Francisco and Coit tower
We continued to discuss the ongoing abuse and the larger issues raised by attacks across the larger internet infrastructure. It’s important to note that even when these attacks aren’t specifically targeting email senders, security issues affect all of us. It’s important for email marketers to understand that increased attacks do affect how customers view the email channel, and senders must take extra care to avoid the appearance of spam, phishing, or other fraudulent activity. I summarized some of the subscription form abuse issues that we’re seeing across the web, and noted responses from Spamhaus and others involved in fighting this abuse. We’re working closely with ESPs and policy groups to continue to document, analyze and strategize best practices to provide industry-wide responses to these attacks.
I was pleased to note that Google is stepping up with a new program, Project Shield, to help journalists and others who are being targeted by these attacks by providing hosting and DDoS protections.
I’m also delighted to see some significant improvements in email client interactions and user experiences. I wrote a bit about some of those here, and I added my thoughts to Al’s discussion of a new user interaction around unsubscribing in the iOS 10 mail client, and I’ll be curious to see how this plays out across other mail clients.
For our best practices coverage, Steve wrote about global suppression lists, and the ways these are used properly and improperly to prevent mail to certain addresses. I wrote about using the proper pathways and workflows to report abuse and get help with problems. I also wrote about the ways in which incentivizing address collection leads to fraud. This is something we really need to take seriously — the problem is more significant than some bad addresses cluttering up your lists. It contributes to the larger landscape of fraud and abuse online, and we need to figure out better ways to build sustainable email programs.
Is there such a thing as a perfect email? I revisited a post from 2011 and noted, as always, that a perfect email is less about technology and more about making sure that the communication is wanted and expected by the recipient. I know I sound like a broken record on this point (or whatever the 21st century equivalent metaphor of a broken record is….) but it’s something that bears repeating as marketers continue to evolve email programs.
We had a bit of a discussion about how senders try to negotiate anti-spam policies with their ESPs. Is this something you’ve experienced, either as a sender or an ESP?
In Ask Laura, I covered shared IP addresses and tagged email addresses, questions I get fairly frequently from marketers as they enhance their lists and manage their email infrastructures. As always, we welcome your questions on all things email delivery related.
Related Posts

A series of tubes

ASeriesofTubes_thumb
The Internet and pundits had a field day with Senator Stevens, when he explained the Internet was a series of tubes.
I always interpreted his statement as coming from someone who demanded an engineer tell him why his mail was delayed. The engineer used the “tube” metaphor to explain network congestion and packets and TCP, and when the Senator tried to forward on the information he got it a little wrong. I do credit the Senator with trying to understand how the Internet works, even if he got it somewhat wrong. This knowledge, or lack there of, drove his policy positions on the issue of Net Neutrality.
In the coming years, I believe we’re going to be seeing more regulations around the net, both for individuals and for corporations. These regulations can make things better, or they can make things worse. I believe it’s extremely important that our elected officials have a working understanding of the Internet in order to make sensible policy. This understanding doesn’t have to be in their own head, they can hire smart people to answer their questions and explain the implications of policy.
Apparently I’m not the only one who thinks it is important for our elected officials to have a working knowledge of technology. Paul Schreiber put up a blog post comparing the website technology used by the current Presidential candidates. Do I really expect the candidate to be involved in decisions like what domain registrar or SSL certificate provider to use? No. But I do expect them to hire people who can create and build technology that is within current best practices.

Read More

September 2014: The Month in Email

September was another busy month for us, but Steve stepped up and wrote a number of really interesting posts on email history, cryptography, and current technical issues in the email landscape.
We started the month with a look at the various RFCs that served as the technical specifications for developing message transfer protocols in the 1970s. It’s really fascinating to look at the evolution of these tools we use every day 40 years later. We followed up with a second post on the origins of network email, which is a great primer (or refresher) on the early days of email.
Steve’s four-part series on cryptography and email started with an in-depth look at how the industry is evolving with respect to encryption and privacy issues. He then introduced us to Alice and Bob (or reintroduced those of us who have been following the adventures of the first couple of cryptography), and described symmetric-key and public-key encryption. His next post described message signing, and how DKIM is used to manage this. He finished up the series with a post on PGP keys.
In industry news: Spamcop is shutting down its email service. There shouldn’t be any major impact on senders, but the post has some specific notes on DMARC implications. We also noted an interesting mail routing suggestion on Twitter, and wrote a post on using Mail.app for this.
In other DMARC news, we wrote about DMARC and report size limits, which might be useful information, depending on your configuration. We also launched a new DMARC tool to help senders understand who is publishing DMARC. Let us know what you think and if you’re finding it useful.
We couldn’t let a month go by without mentioning filters. We looked at a sector we don’t usually discuss, corporate filtering, and went in-depth on a much-misunderstood topic, content filtering.
Finally, Laura offered a webinar on a favorite topic, deliverability, in conjunction with the AMA and Message Systems. If you missed it, you can watch the recorded version here, or just take a peek at some of the reaction via Twitter.

Read More

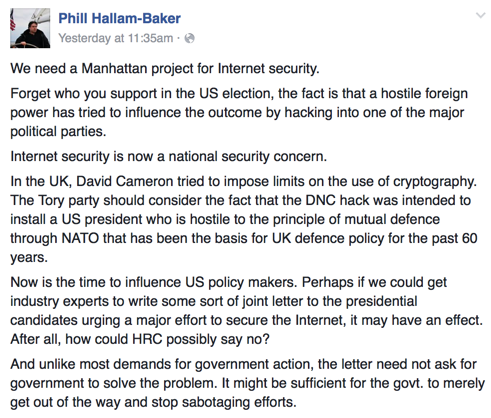
Internet security is national security?

This popped up on my FB feed yesterday.
2016-08-04_16-27-53
What say you? Do we need to create a major effort to improve online security? What challenges do you see to making it work?
Edit: After I published this, I found an article stating that 3.7 million people had their personal health information compromised in a recent attack.

Read More