Google and Amazon and B2B spam

Many of the operational goals of a commercial spammer aren’t related to email delivery at all, rather they revolve around optimizing ROI and minimizing costs. That’s even more true when the spammer isn’t trying to sell their own product, rather they’re making money by sending spam for other companies.
Most legitimate network providers pay at least lip service to not allowing abusive behaviour such as spam from their networks, so a spammer has to make a few choices about what infrastructure to use to optimize their costs.
They can be open about who they are and what they do, and host with a reputable network provider, and build out mailservers much as any legitimate ESP would do. But eventually they’ll get blacklisted by one of the more reputable reputation providers – leading to little of their mail being delivered, and increasing the pressure on their provider to terminate them. They social engineer their provider’s abuse desk, and drag their feet, and make small changes, but eventually they’ll need to move to another provider. Both the delaying tactics and the finally moving are expensive.
Or they can host with a network provider who doesn’t care about abuse from their network, and do the same thing. But they’ll still get blacklisted and, unlike on a more reputable network, they’re much less likely to get any benefit of the doubt from any reputation providers.
Every time they get blacklisted they can move to a new network provider. That’s easy to do if your infrastructure is virtual machine based and moving providers just involves buying a new hosting account. But as anyone who’s heard the phrase “ramping-up” knows mail from new network space is treated with suspicion, and as they’re continually moving their mail won’t reach the inbox much.
Preemptively spreading the sources of your spam across many different IP addresses on different providers, and sending spam out at low enough levels from each address that you’re less likely to be noticed is another approach. This is snowshoe spam and spam filters are getting better at detecting it.
What to do? In order to get mail delivered to the inbox the spammer needs to be sending from somewhere with a good reputation, ideally intermingled with lots of legitimate email, so that the false-positive induced pain of blocking the mailstream would be worse than their spam. That’s one reason a lot of spammers send through legitimate ESPs. They’re still having to jump from provider to provider as they’re terminated, but now they’re relying on the delivery reputation of the shared IP pools at each new ESP they jump to. But that still takes work to move between ESPs. And ESP policy enforcement people talk to each other…
As a spammer you want your mail to be sent from somewhere with good reputation, somewhere you can use many different accounts, so your spam is spread across many of them,  flying below the radar. Ideally you wouldn’t have any documented connection to those accounts, so your activity won’t show up on any aggregated monitoring or reporting.
If nothing in the mail sent out identifies you there is nowhere for recipients to focus their ire. And if recipients can’t tell that the hundreds of pieces of spam in their inbox came from a single spammer, they’re much less likely to focus efforts on blocking that mail stream.
Over the past couple of years I’ve seen a new approach from dedicated B2B spammers, the sort who sell “buy and upload a list, blast out something advertising your company, track responses, send multiple mails over a series of weeks” services to salespeople. They’re the ones who tend to have glossy, legitimate websites, talking about “lead nurturing”, “automated drip campaigns” or “outreach automation”.
They have each of their customers sign up for gmail or google apps accounts, or use their existing google apps accounts, and then the spammer funnels the spam sent on behalf of that customer through that google account. There’s no obvious connection between the spammer and the google account so there’s no risk to the spammer. Google is fairly unresponsive to spam complaints, so as long as the volume sent by each customer isn’t spectacularly high it’s going to be well below Google automation’s threshold of notice.
Google do record where mail that’s injected into their infrastructure in this way comes from, in the Received headers. But the spammers run their sending infrastructure – list management, message composition, tracking and so on – on anonymous, throwaway virtual machines hosted on Amazon’s EC2 cloud, so there’s nothing in the email that leads back to the spammer.
And, for recipients, that’s a problem. Spam filters aren’t going to block this sort of mail, as they can’t easily tell it is this sort of mail. It’s coming from Google MTAs, just like a lot of legitimate mail does. In terms of sheer volume it’s dwarfed by botnet sourced mail or dubious B2B manufacturing spam out of Shenzhen. But, unlike most of that, it’s in your inbox, in front of your eyeballs and costing you time and focus. And that’s much more expensive than network infrastructure or mailbox storage space.
I’m not sure what, if anything, Google or Amazon can do about it at scale, but it’s something that’s going to need to be dealt with eventually.
Meanwhile, if you receive some marginally personalized mail from a sales rep, one attempting to look like 1:1 mail, look at the headers. If you see something like this …

Received: from nordvpnmedia.com (ec2-23-22-26-38.compute-1.amazonaws.com. [23.22.26.38]) by smtp.gmail.com

… at least now you know something about where it came from.
Related Posts

Parasites hurt email marketing

As a small business owner I am a ripe target for many companies. They buy my address from some lead generation firm, or they scrape it off LinkedIn, and they send me a message that pretends to be personalized but isn’t really.
“I looked at your website… we have a list of email addresses to sell you.”
“We offer cold calling services… can I set up a call with you?”
“I have scheduled a meeting tomorrow so I can tell you about our product that will solve all your technical issues and is also a floor wax.”
None of these emails are anything more than spam. They’re fake personalized. There’s no permission. On a good day they’ll have an opt out link. On a normal day they might include an actual name.
These are messages coming to an email address I’ve spent years trying to protect from getting onto mailing lists. I don’t do fishbowls, I’m careful about who I give my card to, I never use it to sign up for anything. And, still, that has all been for naught.
I don’t really blame the senders, I mean I do, they’re the ones that bought my address and then invested in business automation software that sends me regular emails trying to get me to give them a phone number. Or a contact for “the right person at your business to talk to about this great offer that will change your business.”
The real blame lies with the people who pretend that B2B spam is somehow not spam. Who have pivoted their businesses from selling consumer lists to business lists because permission doesn’t matter when it comes to businesses. The real blame lies with companies who sell “marketing automation software” that plugs into their Google Apps account and hijacks their reputation to get to the inbox. The real blame lies with list cleansing companies who sell list buyers a cleansing service that only hides the evidence of spamming.
There are so many parasites in the email space. They take time, energy and resources from large and small businesses, offering them services that seem good, but really are worthless.
The biologically interesting thing about parasites, though, is that they do better if they don’t overwhelm the host system. They have to stay small. They have to stay hidden. They have to not cause too much harm, otherwise the host system will fight back.
Email fights back too. Parasites will find it harder and harder to get mail delivered in any volume as the host system adapts to them. Already if I look in my junk folder, my filters are correctly flagging these messages as spam. And my filters see a very small portion of mail. Filtering companies and the business email hosting systems have a much broader view and much better defenses.
These emails annoy me, but I know that they are a short term problem.  As more and more businesses move to hosted services, like Google Apps and Office365 the permission rules are going to apply to business addresses as well as consumer addresses. The parasites selling products and services to small business owners can’t overwhelm email. The defenses will step in first.
 

Read More

December 2014: The month in email

2014 has been a busy and exciting year at Word to the Wise (look for more on that in a year-end wrap-up post next week!) and this month was particularly thrilling for us as we officially doubled our size with the addition of Josh and Meri on our client services team.
If you’re a regular reader of our blog, you’ve probably spotted Josh’s byline on a few posts: Google’s Inbox Team answers questions on Reddit, which looks at what this new email client portends for both consumers and email marketers, and M3AAWG Recommends TLS, which reviews M3AAWG’s recommendation that mailbox providers phase out SSL encryption in favor of TLS. Look for more smart insights from Josh in 2015.
Steve contributed a post on the proper syntax for displaying a friendly email address, and a very helpful guide for generating useful test data that doesn’t compromise personally identifiable information from your actual customer data. He also detailed the brief DBL false positive from Spamhaus’ new “Abused-Legit” sub-zone and best practices for handling unrecognized responses.
I wrote about some of the subtleties inherent in how brands decide to “converse” with customers in email and other channels. We’ll just keep saying it: companies need to respect the inbox as personal space. I want to thank both Steve and Josh for picking up my slack on blogging. 7+ years is a long time to try and say new things on the blog and I needed a bit of a break.

Read More

Outreach or spam?

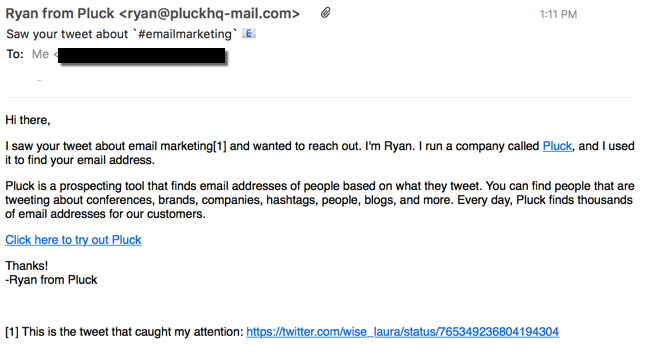
This showed up in my mailbox earlier today:
Pluckyou
The tweet in question
pluckyou2
From Crunchbase: “Pluck is an email prospecting tool that gives you the email addresses of the people tweeting about subjects related to your business.”
Prospecting: another name for spamming. Look, I know that you want to sell you’re newest, greatest product to the world. But just because I tweet something with a # that you think is relevant to your product doesn’t mean that I want to get your spam. I also know it’s hard to get attention and find prospects; I’m a small business owner, too and I need to market my own services. But spamming isn’t a good idea. Ever.
There’s been a significant increase in this kind of spam “to help your business” lately. It’s a rare day I don’t get something from some company I’ve never heard of trying to sell me their newest product. It might be something if they tried a contact or two and then went away. But they’ll send mail for weeks or months without getting an answer. Look, silence IS an answer and it means you need to go away and leave your prospects alone.
Unfortunately, there are services out there that sell a product that let you “automatically follow up” with your prospects. Pluck up there uses one of them, as that’s who’s handling all the links in the message. In fact, if you go to the bare domain (qcml.io) they talk a good anti-spam game. “Die, spammers, die.” I reported the message to them. I’m not expecting them to actually do anything, and I’m not expecting a response.
It’s just spam under another name. There’s no pretense that it’s anything else. Even if it’s sent in a way that makes it look like a real person typed the message, like QuickMail offers. “All emails will come straight out of your personal inbox as though you typed them yourself.” As if you typed them yourself.
The worst part is there’s no real way to stop the mail. I can’t unsubscribe. The companies selling the software don’t provide any guidance to their customers about what the law requires. Take the message from Pluck that started the post. It violates CAN SPAM in multiple ways. Moreover, the address they used is not publicly associated with my twitter handle, which means they’re doing some harvesting somewhere. That means treble penalties under CAN SPAM.
I could reply and ask them to stop mailing me. I’ve done that a couple times with a message that says, “Please don’t email me any more.” I’ve got to tell you, some people get really mad when you ask them not to email you. Some just say yes, but others are really offended that you asked them to stop and get abusive. It’s gotten to the point where I don’t ask any more because of that one person who decides to harass, threaten and scream at me. Sure, it’s maybe 1 in 5, but I don’t have the time or energy to figure out who is going to be receptive and who isn’t. I don’t have time for that. No one has time for that.
I’m expecting that filters are going to catch up eventually and these types of mail will be easier to filter out. Until then, though, small business owners like myself are stuck in a place where we have to deal with spam distracting us from our business. At least I get blog content out of it.


Read More