Way to go Equifax

Earlier this month I wrote about how we can’t trust Equifax with our personal data. I’m not sure we can trust them with a cotton ball. Today, we discover Equifax has been sending consumers worried about their personal information leaking to the wrong site.

[O]n multiple occasions over the span of weeks, the company’s official Twitter account responded to customer inquiries by apparently directing them to a fake phishing site called www.securityequifax2017.com.
Luckily, the fake site — blocked or flagged by many Internet browsers, then taken down Wednesday afternoon — was set up by software engineer Nick Sweeting to educate people rather than steal their information. A banner on the top read: “Cybersecurity Incident & Important Consumer Information Which Is Totally Fake, Why Did Equifax Use A Domain That’s So Easily Impersonated By Phishing Sites?” NPR

Related Posts

Happy New Year!

Well, we mostly survived 2016. A year ago I was making predictions about how 2016 would be the year of email security. I was thinking of things like TLS and authentication and access to the inbox. It wasn’t out of the question, Gmail said they’d be turning on p=reject sometime mid-year. They also were suggesting that they would be putting more value on messages that aligned, even in the absence of a DMARC signature. The first still hasn’t happened, and the second doesn’t appear to be in place, either.
DataSecurity_Illustration
That doesn’t mean email security wasn’t a hot topic in 2016. In fact, the use of a private email server was a major topic during the US elections. We also had spear-phishing play a major role in the compromise of campaign systems. I didn’t talk much about that here when it happened, but news reports make it clear that Chairman Podesta and others were targeted for compromise. The NY Times has a more in depth article with broader context around the attacks and how emails were used to infiltrate a major political party.
The irony is with all the time spent talking about how insecure the private server was, that server wasn’t compromised. Instead, the compromise was at Gmail.
We all need to pay attention to our email and how we use it. It also means when we’re sending bulk and marketing email we need to consider the private and personal information we’re putting in messages. Do you send PII? Is there a way you don’t have to? What can we do to protect our brand and our users?
It’s not just bulk email we need to think about, either. Personal email can contain PII, or personal information. A common saying among some of my security friends is “never put in email anything you wouldn’t want to see on the front page of the Washington Post or NY Times.” That’s an easy thing to say, but the convenience of email makes it easy to share information that we may not want on the front page of either paper. Many of us aren’t actually targets of malicious activity so we don’t have to worry about being targeted the way elected and other officials are. But that doesn’t mean we are not at risk. It just means we’re at less risk than others.
Email is a frequent vector for malicious actors to access computers. Most, if not all of the major breeches in the last few years have started with a phishing attack of some sort. The attacks are planned out and sophisticated. This is not going to get better. The phishers are smart and plan the attacks.  We also need to be more personally aware of security given the current political climate. We need to take steps to protect ourselves more than we have in the past.
Security is more important than ever and we all need to protect ourselves.

Read More
Email address as identity

A few months ago I was talking about different mailbox tools and mentioned email addresses are the keys to our online identity. They are, email addresses are the magic key that authenticates us and opens access to different accounts.
The bad guys know this too. The Justice department recently announced a plea deal related to compromised email accounts. The individual in question gained access to faculty, staff and student email accounts. They then used access to these accounts to access Facebook, iCloud, Google, LinkedIn and Yahoo accounts.
https://twitter.com/pwnallthethings/status/897930523120738304
https://twitter.com/pwnallthethings/status/897931383431061504
https://twitter.com/pwnallthethings/status/897932050111406081
Mediapost published an article this week referencing a survey performed at this year’s BlackHat conference.

Read More

August 2017: The month in email

Hello! Hope all are keeping safe through Harvey, Irma, Katia and the aftermath. I know many people that have been affected and are currently out of their homes. I am proud to see so many of my fellow deliverability folks are helping our displaced colleagues with resources, places to stay and money to replace damaged property.
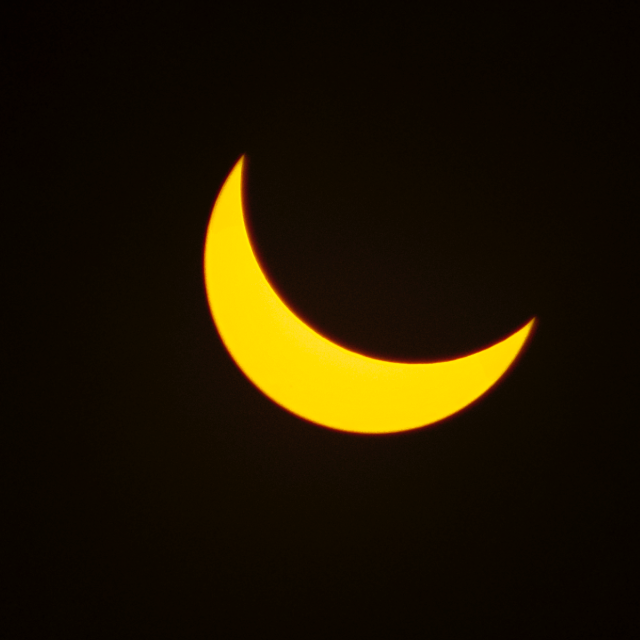
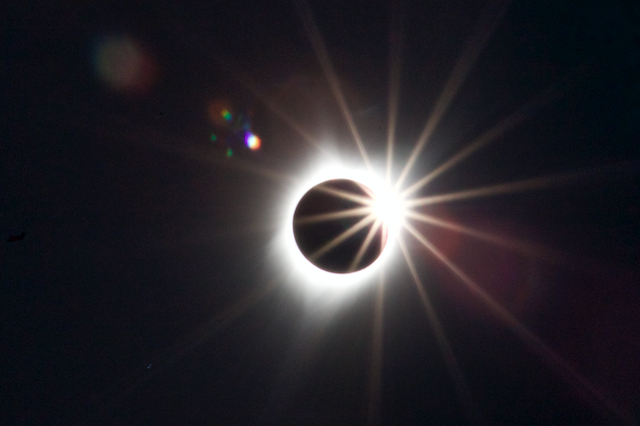
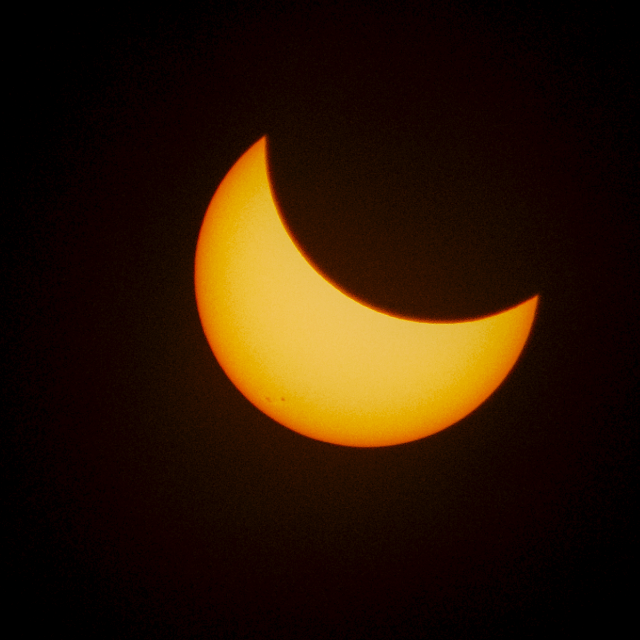
Here’s a mid-month late wrapup of our August blog posts. Our favorite part of August? The total eclipse, which was absolutely amazing. Let me show you some pictures.


Ok, back to email.
We’re proud of the enormous milestone we marked this month: ten years of near-daily posts to our Word to the Wise blog. Thanks for all of your attention and feedback over the past decade!
In other industry news, I pointed to some interesting findings from the Litmus report on the State of Email Deliverability, which is always a terrific resource.
I also wrote about the evolution of filters at web-based email providers, and noted that Gmail’s different approach may well be because it entered the market later than other providers.
In spam, spoofing, and other abuse-related news, I posted about how easy it is for someone to spoof a sender’s identity, even without any technical hacks. This recent incident with several members of the US presidential administration should remind us all to be more careful with making sure we pay attention to where messages come from. How else can you tell that someone might not be wholly legitimate and above-board? I talked about some of what I look at when I get a call from a prospective customer as well as some of the delightful conversations I’ve had with spammers over the years.
In the security arena, Steve noted the ongoing shift to TLS and Google’s announcement that they will label text and email form fields on pages without TLS as “NOT SECURE”. What is TLS, you ask? Steve answers all your questions in a comprehensive post about Transport Layer Security and Certificate Authority Authorization records.
Also worth reading, and not just for the picture of Paddington Bear: Steve’s extremely detailed post about local-part semantics, the chunk of information before the at sign in an email address. How do you choose your email addresses (assuming they are not assigned to you at work or school…)? An email address is an identity, both culturally and for security purposes.
In subscription best practices — or the lack thereof — Steve talked about what happens when someone doesn’t quite complete a user registration. Should you send them a reminder to finish their registration? Of course! Should you keep sending those reminders for 16 months after they’ve stopped engaging with you? THE SURPRISING ANSWER! (Ok, you know us. It wasn’t that surprising.)

Read More